
Instant HTML preview in a sandboxed browser playground
· 5 min read
How online HTML preview works: sandboxed iframes render your markup in milliseconds, with security notes, honest limits, and step-by-step playground usage.
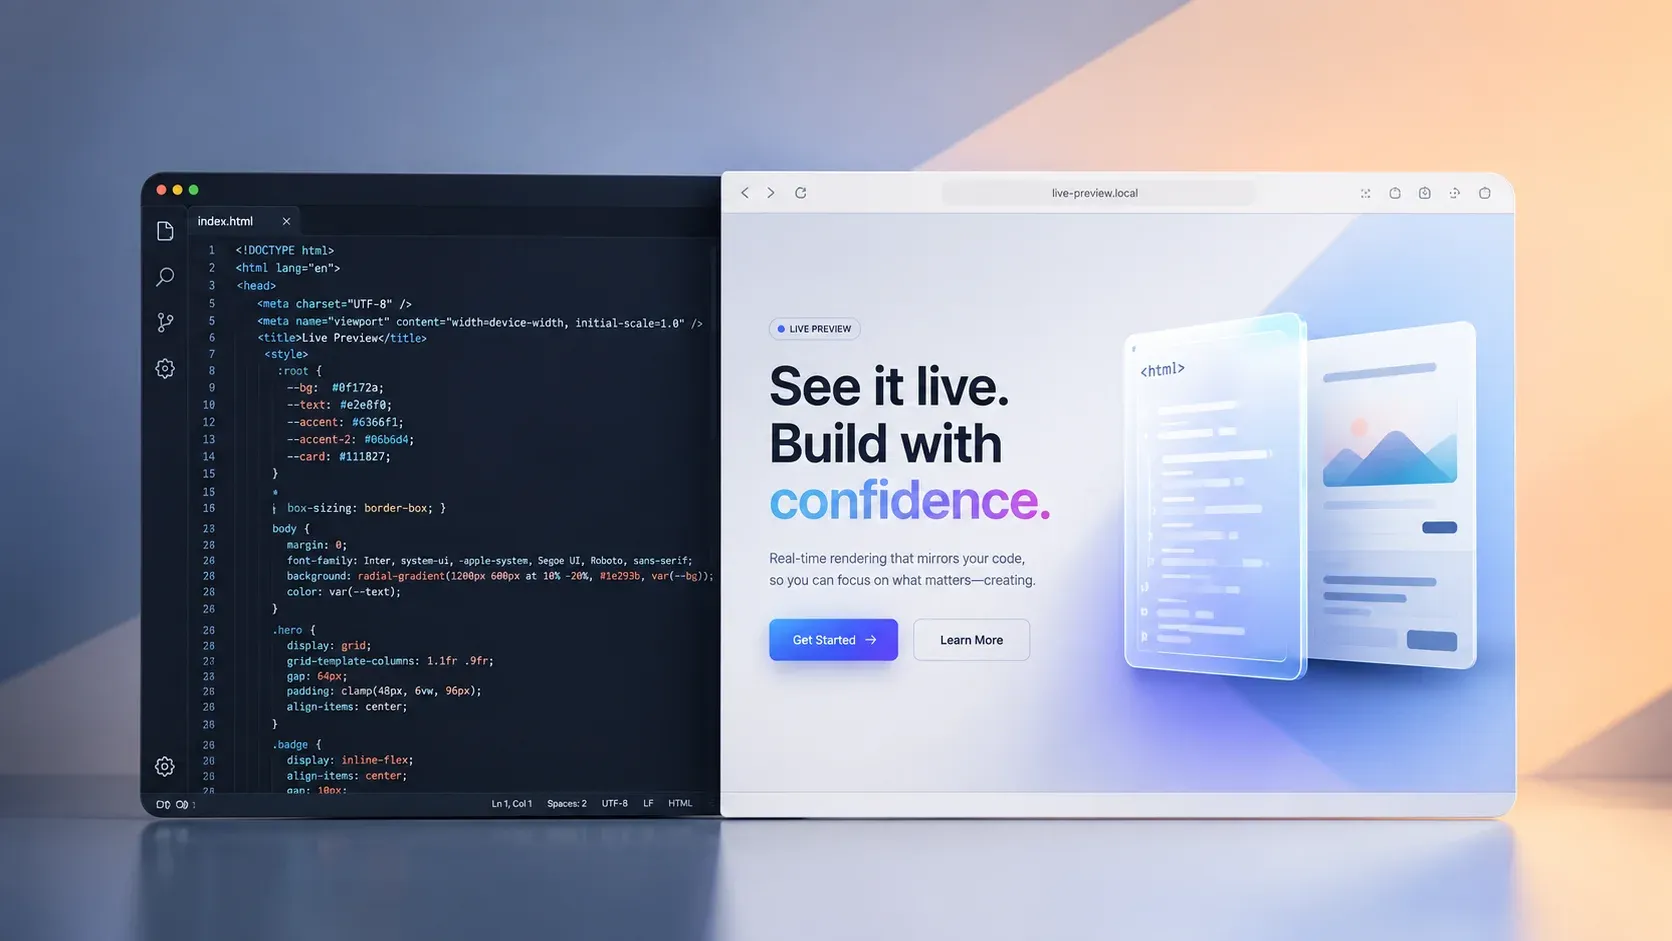
- Live preview tools render HTML in an isolated frame as you type, no files or servers
- Sandboxed iframes keep untrusted markup contained
- Debounced re-rendering keeps typing smooth even on large documents
- Preview covers layout and CSS; cross-browser and email checks need dedicated tools
What a live preview actually does
An online HTML preview takes your markup, renders it in a browser engine, and shows the result beside your code, updating as you type. That rendering path has a specification behind it: the WHATWG iframe spec defines how embedded documents behave. Under the hood the tool writes your source into a sandboxed iframe, the mechanism MDN's iframe documentation describes as a browsing context isolated from the parent page. The isolation is not incidental. You can paste arbitrary snippets, including ones with scripts or broken markup, without endangering the tool itself.
The workflow replaces a heavyweight loop of saving files, switching to a browser, and refreshing. For quick tasks like testing a table structure or checking how entities render, the loop compresses from seconds to zero because the render pane repaints continuously against real browser engines.
Using ToolSura's playground step by step
- Open the HTML CSS playground, which splits editor from rendered output
- Type or paste HTML in the left pane; add CSS in its panel for styling experiments
- The right pane re-renders as you type, typically debounced so mid-word pauses do not flicker
- Iterate until the layout matches intent, then copy the finished code into your project
Because everything runs client-side, snippets never leave the browser, which matters when prototyping with real content such as customer names or unreleased product text that should never transit any server.
Why the sandbox matters more than it sounds
Rendering untrusted HTML inside a normal page would let scripts steal cookies or rewrite the host site. The sandbox attribute restricts scripts, forms, popups, and same-origin access; srcdoc rendering then feeds your exact markup into that frame without a network round trip. One nuance matters: granting both allow-scripts and allow-same-origin together lets framed script reach back into the parent origin, defeating the sandbox entirely, which is why well-built previews omit allow-same-origin. Security-minded developers will recognize the threat model from OWASP's XSS guidance: isolation complements rather than replaces filtering. When your actual application must accept user HTML, our sanitizer tool demonstrates which fragments get stripped before storage, with the sandbox serving as the final containment layer. You can watch this boundary work: paste a snippet whose script reads parent.document and the browser throws a cross-origin error instead of handing over the page, because the frame carries no origin of its own.
srcdoc, blob URLs, and document.write
Each mechanism reaches the same result by a different route. srcdoc writes your source directly into the frame's markup attribute, simple and self-contained. Blob URLs wrap the source in a generated document via createObjectURL, with origin handling that differs from srcdoc's, which is what makes relative fetches possible. Document.write into an empty frame is the legacy route. All three stay client-side, but their origin behavior differs, which is why sandbox tokens matter regardless of path. Stricter deployments layer a Content-Security-Policy on top, per MDN's CSP guide.
What live preview cannot verify
| Concern | Does live preview cover it? |
|---|---|
| Layout and CSS behavior in one engine | Yes, immediately |
| Cross-browser rendering differences | No, single engine only |
| Email client quirks | No; use our email testing guide |
| Accessibility audits | Partially; automated tools still needed |
| Performance under real network conditions | No; profiling required |
Treat preview as the fastest first check, not the last word. That boundary is structural rather than advisory: it comes from the iframe isolation model itself. A snippet that looks perfect in one engine may break in another. Each frame renders through its parent engine and nothing more, so local rendering predicts little about how a marketing email survives Outlook's Word-based engine.
Practical tips for faster iteration
- Paste complete documents including the head section when meta tags affect rendering, such as viewport behavior declared in the document head
- Debug flexbox alignment by toggling one property at a time, following MDN's flexbox guide
- Convert Markdown drafts through the Markdown to HTML converter and preview the result in the HTML live preview
- Test responsive breakpoints by resizing the preview pane instead of guessing widths
- Check entity handling quickly with the entity encoder decoder when special characters misbehave
- For production pages, minify after finalizing using the minifier
- Convert approved mockups to images for stakeholder review via the HTML to image converter
Side-by-side preview tools pair a plain code editor with a live render pane instead of inline WYSIWYG tricks. Inline rich-text fields use the contenteditable attribute that browsers expose globally on every element, which is why modern playgrounds feel native without plugins.
Render early, render often
Previewing HTML online collapses the write-save-switch-refresh cycle into continuous feedback inside a sandboxed frame that keeps experimentation safe. Use it for every layout question before it becomes a committed bug, respect its single-engine limits, and graduate promising work to cross-browser and accessibility checks once the shape looks right.
Written by