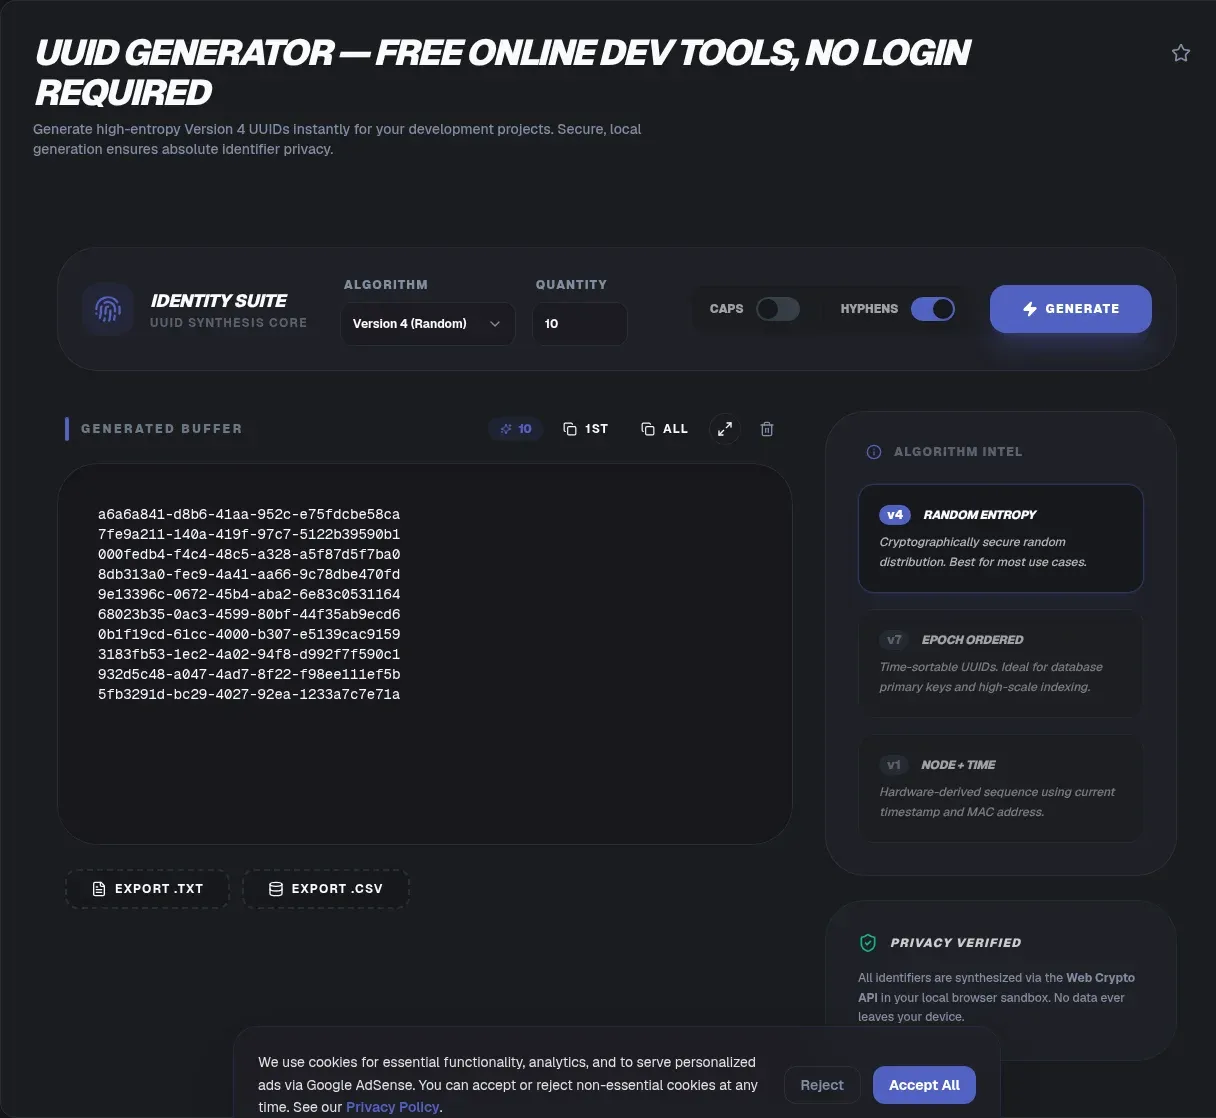
This UUID generator creates random Version 4 identifiers directly in your browser. Click once for a fresh 128-bit ID built from cryptographically secure randomness, copy results one by one, or generate in bulk and download the batch as JSON or CSV. No account stands in the way, and the page keeps working even after your connection drops.
Because everything runs locally, nothing is uploaded and nothing waits on a server round trip. Your browser supplies the entropy through standard Web Crypto interfaces, so privacy rests on verifiable platform behavior rather than on anyone's promise. Ahead you will find how the tool works, the true odds of a duplicate, why time-ordered UUIDv7 is reshaping database keys, and which version fits your project.
Key Takeaways
- A UUID packs 128 bits into the familiar 8-4-4-4-12 hex layout defined by RFC 9562, published May 2024.
- This tool generates Version 4 identifiers client-side with crypto-grade randomness, so nothing is uploaded.
- Reaching a one-in-a-billion collision chance takes roughly 103 trillion properly generated v4 UUIDs.
- For database keys, time-ordered UUIDv7 delivers index-locality gains that can reach one order of magnitude or more.
- Treat UUIDs as identifiers, never as passwords, API keys, or session tokens.
What Is a UUID?
A universally unique identifier (UUID) is a 128-bit label that independent systems can mint separately yet still treat as globally distinct. RFC 9562, the current standard published in May 2024 by authors from Cisco, Uncloud, and the University of Washington, defines eight versions and explicitly obsoletes its 2005 predecessor, RFC 4122 (RFC Editor).
Practically, UUIDs delete coordination from identification. Two servers on different continents, an offline laptop, and a phone app can all produce identifiers without asking any authority whether a value is taken. For distributed systems, PostgreSQL's documentation notes that UUIDs "provide a better uniqueness guarantee than sequence generators" (PostgreSQL).
What Does a Canonical UUID Look Like?
Canonical form reads as 32 hexadecimal digits grouped 8-4-4-4-12 with hyphens, like f81d4fae-7dec-11d0-a765-00a0c91e6bf6, and the standard's grammar permits uppercase, lowercase, or mixed letters (RFC Editor). Mainstream libraries emit this shape consistently, which is why a UUID is recognizable at a glance even before you inspect its version nibble.
Two slots carry metadata rather than identity. The version nibble names which of the eight formats produced the value, and the two variant bits mark it as RFC-defined. Human messiness gets tolerated on the way in: PostgreSQL accepts braces, uppercase, and missing or extra hyphens, yet "output is always in the standard form" (PostgreSQL).
Which UUID Versions Exist, and What Are They For?
Eight versions share the same 128 bits and differ only in how those bits get filled: timestamps, name hashes, or plain randomness (RFC Editor). The table below condenses the catalog into decisions you will actually face.
| Version | Bits Come From | Time-Sortable | Typical Role |
|---|---|---|---|
| v1 | Gregorian timestamp, node ID | Partly | Legacy event logs |
| v2 | DCE Security fields | Partly | Reserved, out of scope |
| v3 | MD5 hash of a name | No | Legacy deterministic IDs |
| v4 | Cryptographic randomness | No | General-purpose default |
| v5 | SHA-1 hash of a name | No | Deterministic IDs |
| v6 | v1 timestamp, reordered | Yes | Migration path from v1 |
| v7 | Unix ms timestamp, randomness | Yes | Modern database keys |
| v8 | Custom vendor formats | Varies | Controlled experiments |
For greenfield designs the specification points one way: implementers should prefer UUIDv7 over UUIDv1 and UUIDv6 wherever possible, guidance stated twice in the document (RFC Editor). Version 2 remains reserved for DCE security deployments you will almost certainly never encounter.
How Does This UUID Generator Work?
The tool delegates randomness to your browser's built-in crypto engine instead of simulating it with ordinary JavaScript. Where supported it calls crypto.randomUUID(), which MDN documents as returning "a v4 UUID using a cryptographically secure random number generator" (MDN). Bulk requests draw raw bytes through crypto.getRandomValues(), part of the W3C Web Cryptography API, whose implementations seed themselves from platform entropy such as the pool behind Unix /dev/urandom (MDN).
Two platform quirks shaped the implementation. getRandomValues() throws QuotaExceededError beyond 65,536 bytes per call, so batches are drawn in chunks (MDN). And crypto.randomUUID() requires a secure context, meaning HTTPS or localhost, though it has been Baseline across browsers since March 2022 (MDN).
Why Does Client-Side Generation Matter for Privacy?
Local processing removes the server from your trust boundary entirely. When identifiers appear inside your own tab, no request log, no database, and no operator sits between you and the output; there is nothing to retain, sell, or breach. Server-side generators can match that only with policy promises, and policies change overnight while architecture does not.
During our August 2026 review of popular generators, uuidgenerator.net cautioned visitors against reusing UUIDs from cached pages, a warning that only makes sense when values are minted remotely. Doing the work on your own device dissolves the entire class of cache-related mistakes.
How Likely Is a UUID Collision?
Vanishingly unlikely, and the numbers deserve careful sourcing. Applying the birthday problem to v4's 122 random bits, as laid out on Wikipedia's UUID entry citing Mathis's 1991 SIAM Review analysis, yields about 2.71 quintillion UUIDs for a 50 percent chance of one collision anywhere, equivalent to generating one billion UUIDs per second for roughly 86 years (Wikipedia).
Smaller thresholds stay absurd. Within 103 trillion properly generated version-4 UUIDs, the chance of a single collision sits near one in a billion by the same computation (Wikipedia). Attribution matters here: these figures come from derived birthday-problem mathematics, not from RFC 9562, which contains no numeric collision estimates at all.
That last clause is the guardrail. The specification mandates cryptographically secure random number generators wherever unguessability matters, so a homemade PRNG seeded from the clock wrecks the guarantee long before birthday math ever could (RFC Editor). Browsers handle this correctly by default.
Why Does UUIDv7 Matter for Database Indexes?
Random keys scatter inserts across a B-tree, forcing page splits everywhere and diluting cache usefulness; time-ordered keys concentrate writes at the hot edge. The RFC calls the performance effects of poor database-index locality potentially dramatic, while gains for monotonic UUIDs over random inserts "can be one order of magnitude or more" (RFC Editor).
Ecosystem support landed quickly. Node.js shipped crypto.randomUUIDv7() in v26.1.0, released May 7, 2026, and its documentation notes the embedded timestamp rides a non-monotonic clock (Node.js release notes, crypto docs). PostgreSQL meanwhile provides native generation for both the UUIDv4 and UUIDv7 algorithms (PostgreSQL). With v7 keys, sorting by ID approximates sorting by creation time, no separate timestamp column required.
What Does a UUIDv7 Look Like, Bit by Bit?
A v7 UUID spends its first 48 bits on a big-endian millisecond Unix timestamp, good until the year 10889, then brackets 74 random bits with version and variant markers (RFC Editor). Laid end to end, the segments fill exactly 128 bits:
unix_ts_ms | ver | rand_a | var | rand_b
 48 bits   | 4   | 12     | 2   | 62
The 12-bit rand_a segment doubles as a counter. Specification rules position it immediately after the timestamp, reseed it randomly on each clock tick, and forbid generators from knowingly returning duplicates after rollover; incrementing by one is discouraged where unguessability matters (RFC Editor). The payoff is an identifier that sorts correctly as raw bytes and stays lexicographically ordered as text.
Is a GUID Different From a UUID?
Functionally, no. A GUID is the identical 128-bit identifier wearing Microsoft-era terminology, and PostgreSQL's documentation remarks that some systems refer to the uuid type as a globally unique identifier (PostgreSQL). Modern systems interoperate because serialization converged on one wire format decades ago.
One fossil survives from the 1990s. RFC UUIDs serialize big-endian, called network byte order, while legacy COM GUIDs serialize several fields little-endian, an exception the specification itself records (RFC Editor). Unless you parse old ActiveX structures byte by byte, the distinction never touches contemporary code.
How Should You Store UUIDs in a Database?
As binary whenever possible. The recommendation is explicit: database applications should store UUIDs as the underlying 128-bit value, which costs 16 bytes against the 36 characters of canonical text, less than half the footprint before indexes even enter the picture (RFC Editor).
PostgreSQL's native uuid column type does this for you: it stores a 128-bit quantity, absorbs untidy human input, and always emits the standard rendering (PostgreSQL). Cornered into string storage anyway? A fixed-length CHAR(36) column beats variable-width alternatives for predictable index behavior.
How Much Information Does a UUID Leak?
That depends entirely on the version. A v1 embeds the generating machine's MAC address beside a precise timestamp, a combination known more for embarrassment than utility. A v7 discloses approximate creation time, because the timestamp is its defining feature. A properly made v4 leaks nothing beyond the bare existence of an identifier (RFC Editor).
Ask what a leaked identifier would teach an attacker before pasting IDs into bug trackers, public repositories, or client-facing payloads. With v4 the honest answer is usually "almost nothing," and v7 exposure merely dates a record. Neither fact moves UUIDs anywhere near the same drawer as credentials.
Where Do UUIDs Belong, and Where Do They Not?
Reach for them wherever independent systems must coordinate identity: distributed object keys, request tracing, idempotency guards, deduplication names, and correlation IDs threaded through service logs. Freedom from a central issuer is the entire design, and no sequence generator can offer it.
Keep them out of authentication. An unguessable identifier is still not a secret, because possession must never equal authorization; the specification's security section exists to keep randomness honest, not to endorse ID-as-password habits (RFC Editor). Dedicated formats such as opaque 256-bit tokens or JWTs fit authentication, and a v1 is predictable by design besides.
Which Version Should You Actually Choose?
Three picks cover nearly every decision. Take v4 as the default for general identifiers. Take v7 when rows should sort by creation time or index locality matters at scale, honoring the standard's stated preference. Take v5 only for deterministic IDs derived from stable names, leaving v3's MD5 construction to legacy code (RFC Editor).
The edges are simple. Versions 1 and 2 trade privacy for features from the 1990s that nobody should ship today, while v8 invites vendors to define custom layouts whose uniqueness must never be assumed. When in doubt, randomness wins.
How Big Is the UUID Ecosystem?
Enormous and measurable. The uuid package logged 285,869,714 npm downloads during the week of August 16 to 22, 2026 per the registry API (npm registry API). Read that as infrastructure-scale adoption rather than a popularity contest: registry totals are inflated by transitive dependency installs and do not represent unique users.
Platform built-ins keep shrinking the dependency's job. Node.js gained crypto.randomUUID() back in the v14 era, a rollout whose version history grew tangled enough that maintainers cataloged the confusion in issue #40037 (GitHub issue, Node docs). Front end and back end now share one calling convention, no package required.
How Does ToolSura Compare With Other UUID Generators?
Every major generator mints valid identifiers, so the honest differentiators are processing location, version coverage, and disclosure quality. Our snapshot of search results on August 24, 2026 placed uuidgenerator.net and uuidtools.com in the top spots, bulk generation nearly universal, and public APIs offered by two of the leaders.
Privacy disclosure varies the most. guidgenerator.com states "We don't store the UUIDs you generate," though it does not disclose on its homepage whether generation happens client-side or server-side. uuidtools.com makes no privacy or storage claims and does not state where generation occurs, and it showed no v7 generator during our review. We report what pages disclose and decline to speculate about the rest.
Where this page differs is candor and depth. ToolSura's generator produces Version 4 exclusively and says so plainly, states its client-side architecture up front, exports batches as JSON or CSV, and pairs the tool with sourced explainers, including the collision arithmetic and the v7 transition above, that reviewed competitors did not attempt.
The Bottom Line
A UUID looks trivial until you ask why it works: 128 carefully budgeted bits, a version system that encodes intent, and collision odds so remote they border on the philosophical. Generate v4 identifiers above at no cost, store them as binary, move to v7 when your indexes demand order, and confirm any suspicious string with the validator below. Bookmark this page for the math as much as the tool.
Related Tools
Round out your identifier workflow with these companions:
- UUID Validator for format checks and automatic version detection
- Base62 Encoder/Decoder for squeezing a 128-bit ID into 22 compact characters
- Timestamp Converter for decoding the Unix milliseconds inside UUIDv7 values
- JSON Formatter & Validator for tidying API payloads that carry UUID fields
- Regex Tester for building extraction patterns around UUID-shaped strings
- Word Counter for drafting conventions documents in measured prose
- UUID v4 vs v7 — which to use for ordered IDs
When you need fresh identifiers, the UUID Generator is one click away."